
Attack Surface Management Market Size, Share, Trends & Forecast, 2026–2034
REPORT DETAILS
Attack Surface Management Market Summary
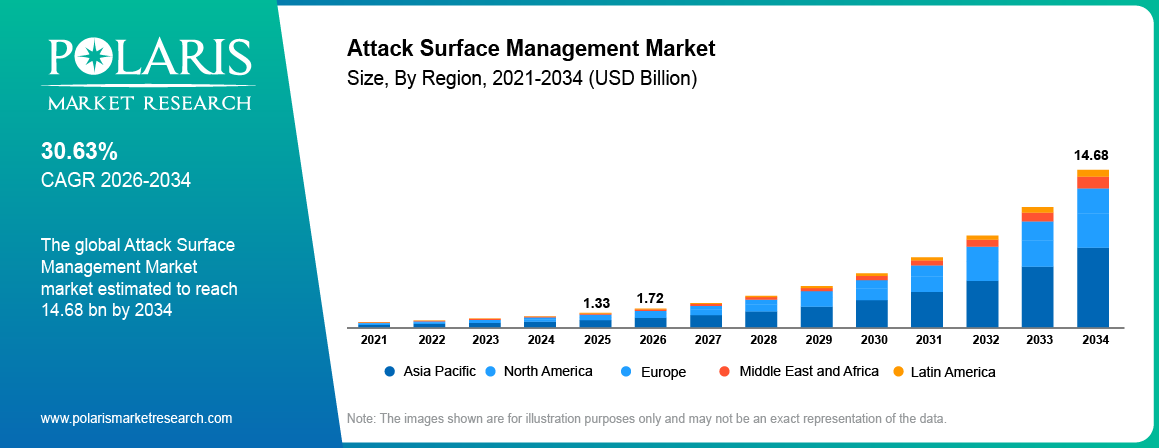
Attack surface management market size was valued at USD 1.33 billion in 2025. The market is expected to grow at a CAGR of 30.63% from 2026 to 2034. Market growth is driven by expanding cloud and IoT environments and rising cyber threats. Also, increasing EASM adoption and the need for continuous visibility into known and unknown digital assets boost the expansion.
Market Statistics
Key Takeaways
- North America held the leading market share of 40.84% in 2025, due to heavy investment in cybersecurity, digital infrastructure, and enterprises.
- The market in Asia Pacific is estimated to register the highest CAGR of 32.65% during the forecast period, owing to growing cloud adoption, digital transformation, and investments in cybersecurity.
- The solution segment led with 67.35% share in 2025, driven by growing needs for automated asset discovery, continuous monitoring, and digital risk protection.
- The BFSI segment accounted for the largest revenue share of 26.34% in 2025. This is due to compliance with security requirements, digital assets, and cybersecurity risks.
- The cloud deployment segment is expected to record the highest CAGR of 31.50% during 2025–2030. Increasing focus on cloud security posture management (CSPM) will boost segment growth.
Note: Figures and projections outlined in this report are the result of Polaris Market Research’s proprietary analytical processes, grounded in the latest available datasets and market observations.
What is Attack Surface Management?
Attack surface management (ASM) is the continuous discovery, monitoring, inventorying, and assessment of internet-accessible assets, cloud resources, applications, devices, and other digital infrastructure owned by an organization. Rather than relying on an existing asset list, ASM assesses what is available through the eyes of a potential attacker and discovers unknown, unmanaged, or forgotten assets.
ASM helps organizations address cyberattack risks to their assets. IT inventories typically list assets the organization knows about and has recorded. ASM helps identify assets that were not listed before, such as shadow IT, unknown subdomains, exposed cloud instances, test environments, and unmanaged applications.
ASM is an ongoing process of discovering and classifying assets, identifying vulnerabilities, and conducting risk assessments. It also prioritizes risks and conducts remediation. This process repeats with every newly discovered asset or system configuration change. That is how ASM differs from one-time security auditing or penetration testing.
External attack surface management (EASM) is a closely related area that focuses mainly on internet-facing assets. Cyber Asset Attack Surface Management (CAASM) provides broader visibility into internal and external assets by bringing information from multiple security and IT systems together. ASM can also support wider exposure management programs by helping organizations understand which assets and weaknesses could create the greatest business risk.
With the increasing use of cloud services, IoT modules, software as a service applications, remote infrastructure, application programming interfaces, and third-party platforms by businesses, the list of assets to monitor continues to grow. It increases the need for continuous asset discovery, risk assessment, and remediation.
How Attack Surface Management Works
ASM generally follows a continuous cycle:
- Asset discovery: Identify all known and unknown systems, domains, applications, cloud assets, devices, and other types of digital assets.
- Asset Inventory Creation: Create the asset inventory and map it to the business and security information.
- Exposure Analysis: Discover vulnerabilities, misconfigurations, exposed services, outdated software, and many more.
- Risk assessment: Prioritize the security risks based on several considerations, such as criticality of the asset, exploitability, exposure, and impact on the business.
- Problem resolution: Share the prioritized findings with the security team, IT team, and development team to resolve the issues.
- Continuous monitoring: Conduct this activity continuously since the assets, configuration, applications, and threats change all the time.
This continuous approach helps organizations identify new exposure sooner and reduce the time between discovering a security issue and taking action.
Attack Surface Management vs Vulnerability Management
Attack surface management has some overlap with vulnerability management (VM), but these two have different objectives. ASM’s purpose is to discover and profile assets that could become a potential target of attackers. However, vulnerability management helps find and fix vulnerabilities that exist in known assets.
| Attribute | Attack Surface Management (ASM) | Vulnerability Management (VM) |
| Primary focus | Discovering and inventorying known and unknown exposed assets | Scanning known assets for vulnerabilities and misconfigurations |
| Starting point | Outside-in view of the organization | Existing internal asset inventory |
| Core output | Continuously updated view of assets and exposure | Prioritized list of vulnerabilities and remediation actions |
| Risk context | Considers asset exposure, business importance, exploitability, and other factors | Primarily focuses on vulnerability severity and remediation |
| Relationship | Helps identify assets and exposures that may need further security assessment | Helps remediate vulnerabilities found on known assets |
Source: Polaris Market Research Analysis
Thus, ASM and VM are complementary to each other. The former can help in identifying the assets that might go unnoticed by the security team during vulnerability management, while the latter can assist in resolving any vulnerabilities identified through the former process.
Market Dynamics
Drivers: Rising IoT Integration
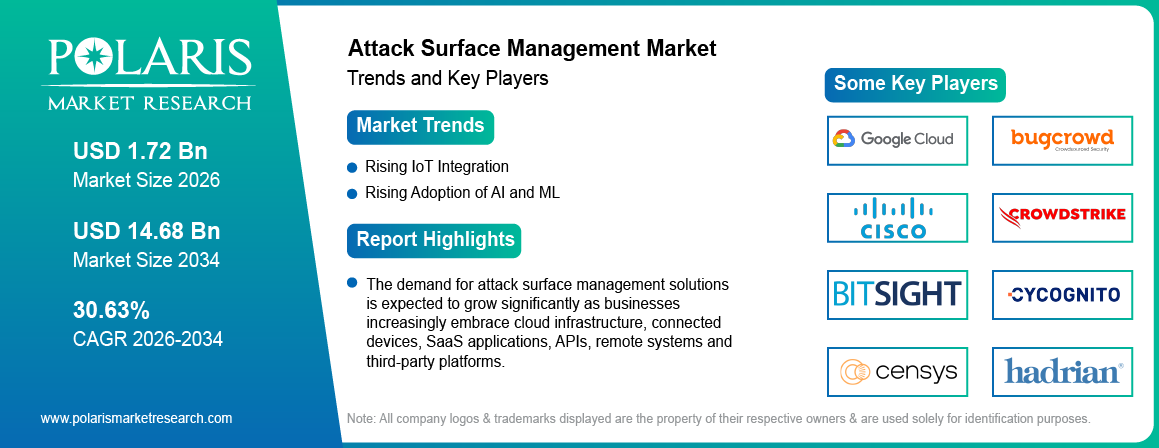
Key players worldwide are increasingly aware of the challenges of attack surface management. Hence, they are integrating dedicated capabilities for IoT asset discovery and vulnerability assessment. It focuses on creating strong mechanisms that can effectively identify, assess, and handle the security of IoT devices within an organization's digital ecosystem. GSMA Intelligence predicts IoT connections to reach 38 billion by 2030, out of which 60% will be from the enterprise sector. This evolution ensures the security team can tackle the specific security issues across different types of IoT devices. Thus, increasing IoT integration drives the growth of the market (Source: gsmaintelligence.com).
Drivers: Rising Adoption of AI and ML
Advancements in AI and ML boost the development of attack surface management. It leads to the introduction of predictive analysis, anomaly detection, and automated response actions. According to Stanford University, generative AI (GenAI) technology reached 53% population adoption in just three years. For U.S. consumers, the estimated value of GenAI tools reached USD 172 billion annually by early 2026. Its median value per user tripled between 2025 and 2026. These advancements enable security teams to go beyond reactive measures and can foresee potential threats. Technological advancements and analytics to promptly identify and eliminate threats in real time are possible. By integrating these capabilities, organizations can respond quickly to known threats and proactively anticipate and overcome emerging challenges. Rising emphasis on AI Security Operations drives the demand for attack surface management solutions (Source: hai.stanford.edu).
Drivers: Cloud Adoption Expanding Attack Surfaces
The rapid growth of public, private, and hybrid cloud platforms has resulted in many more assets that organizations have to discover and protect. The cloud account, workload, storage, API, container, application, and identity can always undergo changes. Therefore, the traditional asset inventory becomes a complex process. The ASM solutions aid the security team in maintaining visibility through the evolution of the cloud platform. Furthermore, the growing adoption of multi-cloud environments increases the need for centralized asset discovery and risk assessment across different cloud platforms.
Restraint: Complexity of Digital Ecosystems
Modern organizations operate in diverse, interconnected environments that include cloud services, IoT devices, and third-party applications. This complexity exponentially expands the attack surface, making it difficult to obtain a comprehensive view of all potential vulnerabilities and threats. Moreover, the dynamic nature of digital ecosystems, characterized by frequent updates, configuration changes, and new deployments, complicates the task of maintaining an accurate and up-to-date understanding of the attack surface. Consequently, organizations struggle to prioritize and address security risks effectively, increasing exposure to cyber threats and potential data breaches.
Opportunity: Integration with Unified Exposure-Management Platforms
There is an increasing emphasis on integrating ASM with unified exposure-management platforms. It creates lucrative opportunities for vendors to provide centralized visibility across external assets, vulnerabilities, cloud environments, and other security exposures. This helps organizations prioritize risks based on their cumulative exposure.
Challenges in Attack Surface Management Market
- Limited Visibility of Assets: Inability to locate assets from subsidiaries, contractors, acquisitions, and other third parties.
- Rapidly Evolving Assets: Cloud assets, applications, APIs, and other connected devices are easily provisioned, configured, and decommissioned.
- Large Volume of Findings: Security teams receive more findings than they can handle manually.
- Integration Requirements: ASM solutions are normally required to integrate with vulnerability management, cloud security, identity, IT service management, and other security solutions.
- Security Staffing Constraints: The organization has fewer security experts and an insufficient budget to monitor its attack surface.
Segmentation Analysis
The market is primarily segmented based on offering, application, deployment mode, organization size, end user, and region.
By Offering Analysis
The solutions segment led the market with a substantial revenue share of 67.35% in 2025. The dominance is largely attributable to its ability to thoroughly identify, evaluate, and address potential vulnerabilities within its digital infrastructure. This method involves the use of advanced software like vulnerability scanners, penetration testing tools, and threat intelligence systems to examine the attack surface. Furthermore, organizations enforce strong configuration management practices to ensure that all systems and applications comply with security best practices and regulatory requirements.
The services market segment is expected to record a CAGR of 31.48% during the forecast period. The growth is fueled by comprehensive assessments, penetration testing, and red team engagements. Skilled cybersecurity professionals conduct the process to identify and exploit potential weaknesses in the organization's digital infrastructure. Additionally, managed security services providers (MSSPs) offer ongoing monitoring, threat intelligence analysis, and incident response support to detect and mitigate security threats across the attack surface proactively. Furthermore, consulting services provide strategic guidance and customized solutions to optimize attack surface management processes, align security initiatives with business objectives, and enhance overall cybersecurity posture.
By Deployment Mode Analysis
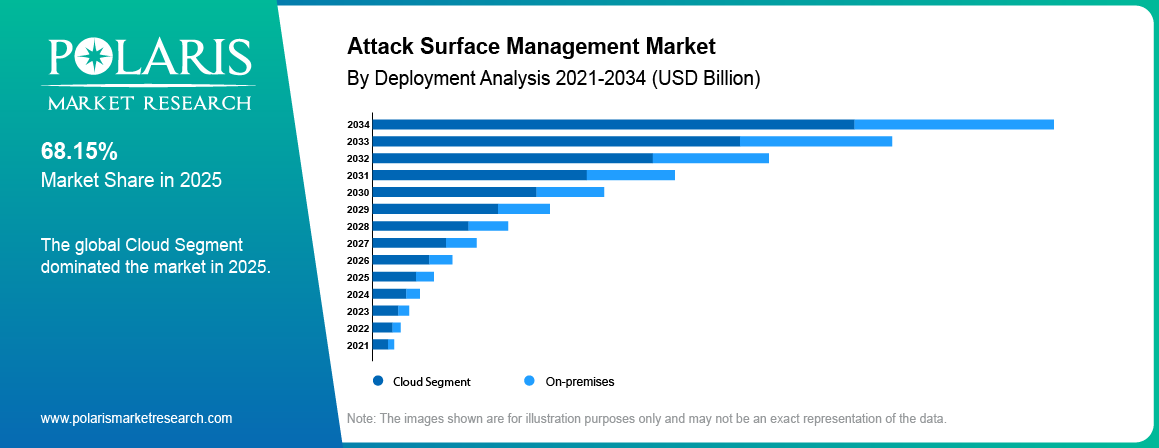
The cloud segment dominated the market with 68.15% share in 2025. Cloud-based solutions offer scalable and centralized monitoring of digital assets. It enables real-time detection and response to security threats across diverse environments. These platforms provide enhanced visibility, automation, and collaboration, thereby streamlining risk assessment and mitigation efforts for a stronger cybersecurity posture. Also, rising emphasis on cloud security posture management (CSPM) will drive the segment growth.
The on-premises segment is expected to grow at significant CAGR of 28.60% during forecast period. On-premises solutions allow for detailed customization and integration with current security frameworks, facilitating personalized risk evaluations and swift responses to emerging threats. This method provides direct oversight of hardware, software, and network setups. It ensures that sensitive data remains within the organization's confines. On-premises solutions may necessitate a substantial initial investment and continuous upgrades.
By Organization Size Analysis
Large enterprises accounted for a dominant market share of 62.48% in 2025. Large enterprises have more complicated IT infrastructure, due to their presence across many geographical locations, clouds, business units, subsidiaries, and third parties. These enterprises need continuous asset discovery and risk monitoring to maintain visibility across a wide range of attacks.
The SMEs segment is expected to register a higher CAGR of 31.63% during the projected period. This is due to the increasing adoption of cloud, remote working, SaaS apps, and other connected devices in small organizations. Cloud-based ASM solutions would provide SMEs with continuous asset monitoring without heavy security investment.
By End-User Analysis
The BFSI (Banking, Financial Services, and Insurance) segment held a significant market share of 26.34% in 2025. The dominance is attributed to the rising emphasis on complying with strict regulatory demands. BFSI organizations comprise valuable assets that require a specialized cybersecurity approach. BFSI organizations conduct comprehensive risk assessments and compliance audits to meet industry standards such as GDPR and PCI DSS. Collaborating with cybersecurity professionals and participating in information-sharing initiatives within the sector bolsters the resilience of BFSI entities against emerging cyber risks.
The IT & ITeS segment is register the significant CAGR of 31.37% during the forecast period. This is due to companies utilizing a variety of technologies and platforms to oversee, evaluate, and minimize security threats within their digital framework. This includes implementing advanced security measures like intrusion detection systems, endpoint protection software, and network monitoring tools to identify and address possible risks. Furthermore, thorough vulnerability assessments and penetration tests are carried out to pinpoint flaws in software, hardware, and network setups.
Attack Surface Management Use Cases
- Asset Discovery: Identifies known, unknown, and internet-facing assets.
- Shadow IT Discovery: Finds unauthorized applications and cloud services.
- Vulnerability Prioritization: Helps prioritize exposed vulnerabilities based on risk.
- Cloud Monitoring: Tracks security exposures across cloud environments.
- Third-Party Risk: Monitors external assets linked to vendors and suppliers.
- Threat Intelligence: Detects malicious infrastructure and emerging threats.
- Compliance Management: Supports asset visibility and security compliance.
- M&A Assessment: Identifies security risks across acquisition targets.
- Continuous Monitoring: Tracks changes in assets and external exposures.
Key Areas of Attack Surface Management Market
External Attack Surface Management (EASM)
External Attack Surface Management (EASM) refers to assets visible or accessible to an organization from outside. Such assets may include domains, subdomains, public cloud assets, websites, APIs, exposed services, certificates, applications, and many other internet-facing assets.
Organizations usually lack complete visibility into all assets exposed on the internet, propelling the need for EASM. Factors like business growth, cloud migrations, M&A activities, remote working environments, third-party services, and shadow IT are creating new external assets that are unknown to the security teams.
EASM software continuously scans and monitors assets, identifying vulnerabilities, misconfigurations, open services, expiring certificates, and other threats. This methodology provides a broader view of the company's digital footprint from the outside and can complement existing asset and vulnerability management efforts.
The growing focus on continuous threat exposure management (CTEM) is increasing the role of EASM. Organizations are increasingly looking to identify the exposures most likely to be exploited rather than treating every vulnerability with the same level of priority.
Role in Threat Exposure Management
Attack surface management is becoming an integral part of the larger concept of exposure management. Instead of treating vulnerabilities as isolated technical issues, organizations are bringing together asset information, vulnerabilities, cloud risks, identities, attack paths, and threat intelligence. It helps them understand which exposures could create the greatest business risk.
ASM offers the asset and exposure visibility required to accomplish this task. It enables discovery of new assets, links them to security findings, and allows prioritization of actions based on the probability and consequences of attack.
This trend toward continuous threat exposure management is also driving companies to shift from periodic assessments to continuous monitoring and threat remediation.
Cyber Risk Management for Business Leaders
For corporate leaders, ASM helps them understand how shifts in the digital space can influence their cyber risks. New cloud apps, acquisitions, remote IT, device connectivity, and third-party applications increase risk even with security measures in place.
ASM can help management teams track areas such as:
- Number of known and unknown assets
- Internet-facing assets and high-risk exposures
- Critical vulnerabilities requiring immediate action
- Changes in the external digital footprint
- Exposure associated with subsidiaries and third parties
- Progress in reducing high-priority risks
This allows cybersecurity teams to communicate security exposure in business terms rather than relying only on technical vulnerability counts.
Regional Insights
The fragmentation of attack surface management by region includes North America, Europe, Asia Pacific, Latin America, and the Middle East & Africa.
North America
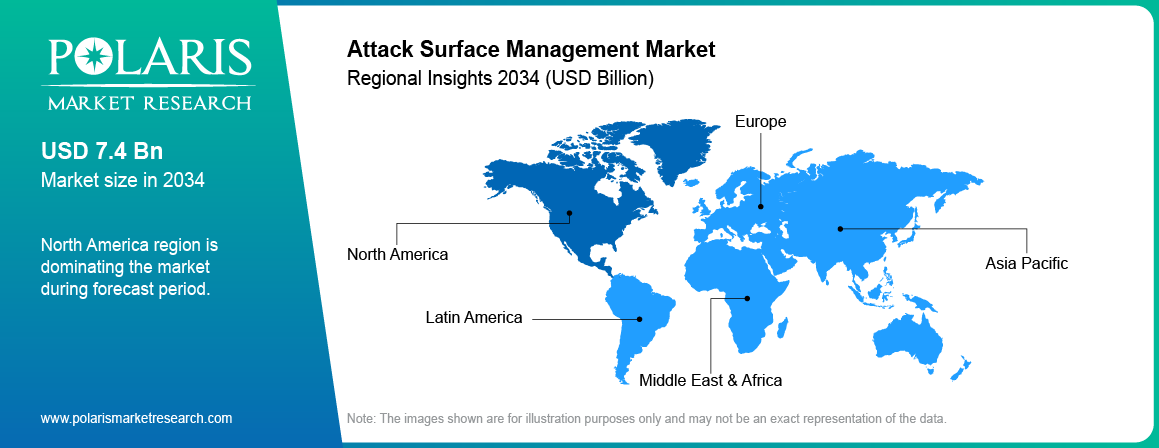
North America dominated the global attack surface management market share with 40.84% revenue share in 2025. The growth of the segment market can be largely attributed to the rapid increase in conducting an analysis of the attack surface. It helps identify risks and weaknesses within the infrastructure. Such analysis enables teams to prioritize and address issues effectively. By uncovering unmanaged assets and other hidden risks, the implementation of impactful solutions can enhance security with minimal resource allocation. It assists in identifying all the external assets, including shadow IT, neglected infrastructure, and configuration errors. Using automated discovery of IT assets in order to continuously identify the attack surface of the organization boosts the North America attack surface management market growth.
Asia Pacific
The Asia Pacific attack surface management market is expected to record the highest CAGR of 32.65% during the forecast period. The growth is supported by rapid cloud adoption and expanding digital infrastructure. Also, increasing use of connected devices and rising cybersecurity investments across major economies propel the regional market growth. In April 2026, Microsoft announced an investment worth USD 10 billion in Japan from 2026 through 2029. It includes cybersecurity collaboration along with AI infrastructure that helps enhance cyber resiliency. Furthermore, organizations from other nations like China, Japan, India, South Korea, and Australia are paying more attention to continuous asset visibility as they increasingly rely on cloud-based applications and services (Source: microsoft.com).
Europe
The Europe attack surface management market is projected to record the significant CAGR of 29.85% during the projected period. The growth is attributed to increasing needs for cybersecurity, stringent data protection rules, cloud usage, and digital resilience. According to the European Union Agency for Cybersecurity (ENISA), threats to availability accounted for 46% of cyber threats in the EU, while ransomware held 27% and threats to data contributed to 16%. Organizations are increasingly adopting ASM to improve asset visibility, manage external exposure, and strengthen risk management across complex digital environments (Source: consilium.europa.eu).
Emerging Technologies in Attack Surface Management
- AI and ML: Improve asset discovery, risk detection, and prioritization.
- Agentic AI: Automates exposure analysis and remediation recommendations.
- CTEM: Enables continuous identification and prioritization of security exposures.
- Attack Path Analysis: Identifies relationships between assets, vulnerabilities, and attack paths.
- Cloud-Native ASM: Monitors assets across cloud, SaaS, and container environments.
- EASM: Discovers internet-facing and unknown digital assets.
- CAASM: Combines asset data from multiple security and IT systems.
- Security Graphs: Connect assets, identities, and vulnerabilities for better risk visibility.
Competitive Landscape
The attack surface management market is fragmented and is anticipated to witness competition due to several players' presence. Major attack surface management vendors in the market are constantly upgrading their technologies to stay ahead of the competition. They emphasize ensuring the efficiency, integrity, and safety of the customer’s data. These players focus on technology, product upgrades, and collaboration to gain a competitive edge over others in this domain to capture a significant market share.
Competition is increasingly moving toward broader exposure management platforms. Leading cybersecurity vendors are combining asset discovery with vulnerability management, cloud security, threat intelligence, attack-path analysis, AI-based prioritization, and automated remediation.
List of Key Companies
- Bitsight
- Bugcrowd
- Censys
- Cisco
- CrowdStrike
- CyCognito
- Google Cloud
- HackerOne
- Hadrian
- IBM
- IONIX
- Microsoft (RiskIQ)
- Outpost24
- Palo Alto Networks
- Qualys
- Rapid7
- SecurityScorecard
- Tenable
- Trend Micro
- UpGuard
Market Positioning
| Positioning Tier | Representative Vendors | Typical Strength |
| Platform leaders | Palo Alto Networks (Cortex Xpanse), Microsoft (RiskIQ-derived), CrowdStrike (Falcon Surface) | Broad platform integration, large existing customer base |
| Pure-play EASM specialists | CyCognito, Censys, IONIX, Hadrian | Deep external-asset discovery depth, faster feature cadence |
| Vulnerability/exposure-management incumbents | Tenable, Qualys, Rapid7 | Strong tie-in to existing vulnerability-management workflows |
| Risk-rating / third-party-risk players | Bitsight, SecurityScorecard, UpGuard | Vendor and supply-chain risk scoring as a differentiator |
| Crowdsourced/offensive-security players | Bugcrowd, HackerOne | Human-augmented discovery via bug bounty and pentest networks |
Source: Polaris Market Research Analysis
Recent Developments
- September 2026: CYFIRMA signed a strategic partnership with RAH Infotech to advance preemptive cybersecurity across India. (Source: cyfirma.com)
- In August 2026, Tenable Holdings, Inc. announced advanced AI security capabilities within the Tenable One Exposure Management Platform. It will expand its coverage across major LLMs such as Google Gemini, OpenAI ChatGPT Enterprise, Anthropic Claude, and Microsoft Copilot. Its capabilities offer security teams an extended view of where AI is being used, what risk it creates, and where action is required. (Source: tenable.com)
- In July 2026, Infoblox entered the external attack surface management (EASM) market with DNS-native visibility. It helps support the continuous discovery and prioritization of internet-facing exposures and third-party risks. (Source: infoblox.com)
- In July 2026, Zscaler partnered with Schwarz Digits to deliver sovereign Zero Trust SASE in Europe. This will help organizations reduce their attack surface and prevent lateral threat movement. (Source: zscaler.com)
- In April 2025, Marlink launched External Attack Surface Management (EASM) solution that can provide customers a proactive cyber threat detection. (Source: marlink.com)
Future Outlook
The demand for attack surface management solutions is expected to grow significantly as businesses increasingly embrace cloud infrastructure, connected devices, SaaS applications, APIs, remote systems and third-party platforms. A major driver of the attack surface management market growth is expected to be the necessity to identify unknown assets and monitor external exposure on a continuing basis.
The market is shifting toward broader exposure management. ASM platforms are increasingly being connected with vulnerability management, cloud security, identity security, threat intelligence, and attack-path analysis. AI and automation are expected to further improve risk prioritization and remediation.
Over the forecast period, competition is likely to shift from standalone asset discovery tools toward integrated platforms that can discover assets, understand risk, prioritize exposures, and support remediation through a single workflow.
Research Methodology
This research uses top-down and bottom-up approaches to estimate and forecast the global Attack Surface Management market. Secondary research covers company reports, regulatory filings, product announcements, industry publications, cybersecurity databases, and other reliable sources to assess market trends, segments, competition, and regional developments.
The primary research supports the secondary research through interaction with the suppliers of cybersecurity solutions, enterprise consumers, technology leaders, system integrators, and other industry stakeholders that provide insight into adoption trends, market dynamics, market segment growth, and regional variations.
Market sizing combines supply-side vendor revenues and demand-side cybersecurity spending across organization sizes, deployment models, applications, industries, and regions. Estimates are cross-checked against available industry and company-level evidence, with market size and CAGR figures re-verified during scheduled report updates.
Attack Surface Management Market Segmentation
By Offering Outlook (Revenue, USD Billion, 2021–2034)
- Solutions
- Services
By Solution Type Outlook (Revenue, USD Billion, 2021–2034)
- Asset Discovery & Inventory
- Risk Assessment
- Continuous Monitoring
- Reporting & Analytics
- Others
By Application Outlook (Revenue, USD Billion, 2021–2034)
- Asset Discovery & Inventory
- Continuous Monitoring
- Vulnerability Management
- Threat Intelligence
- Reporting & Analytics
- Risk & Compliance Management
- Others
By Deployment Mode Outlook (Revenue, USD Billion, 2021–2034)
- Cloud
- On-Premises
By Organization Size Outlook (Revenue, USD Billion, 2021–2034)
- Large Enterprises
- Small and Medium-Sized Enterprises (SMEs)
By End-User Outlook (Revenue, USD Billion, 2021–2034)
- BFSI
- IT & ITeS
- Government & Defense
- Retail & eCommerce
- Energy & Utilities
- Education
- Others
By Regional Outlook (Revenue, USD Billion, 2021-2034)
- North America
- U.S.
- Canada
- Europe
- Germany
- France
- UK
- Italy
- Spain
- Netherlands
- Russia
- Rest of Europe
- Asia Pacific
- China
- Japan
- India
- Malaysia
- South Korea
- Indonesia
- Australia
- Vietnam
- Rest of Asia Pacific
- Middle East & Africa
- Saudi Arabia
- UAE
- Israel
- South Africa
- Rest of Middle East & Africa
- Latin America
- Mexico
- Brazil
- Argentina
- Rest of Latin America
Attack Surface Management Market Report Scope
| Report Attributes | Details |
| Market Size in 2025 | USD 1.33 Billion |
| Market Size in 2026 | USD 1.72 Billion |
| Revenue Forecast by 2034 | USD 14.68 Billion |
| CAGR | 30.63% from 2026 to 2034 |
| Base Year | 2025 |
| Historical Data | 2021–2024 |
| Forecast Period | 2026–2034 |
| Quantitative Units | Revenue in USD Billion and CAGR from 2026 to 2034 |
| Report Coverage | Revenue Forecast, Competitive Landscape, Growth Factors, and Industry Trends |
| Segments Covered |
|
| Regional Scope |
|
| Competitive Landscape |
|
| Report Format |
|
| Customization | Report customization as per your requirements with respect to countries, regions, and segmentation. |
Source: Polaris Market Research Analysis
Report Coverage
The attack surface management market report emphasizes key regions across the globe to provide better understanding of the product to the users. The report provides market insights into recent developments, trends, and technologies gaining traction across major markets. Furthermore, the report covers qualitative analysis of the major factors influencing adoption, including cloud migration, IoT adoption, AI, external exposure, and the shift toward continuous exposure management.
The report provides detailed analysis of the market while focusing on key aspects such as competitive analysis, offering, organization size, deployment mode, application, end-user, regional trends, and future growth opportunities.
Attack Surface Management Market FAQ's
The market is projected to grow from USD 1.33 billion in 2025 to USD 14.68 billion by 2034, at a 30.63% CAGR. Rising adoption of IoT and cloud drives the market growth.
North America led the global market with 40.84% in 2025. The dominance is fueled by increasing investments in cybersecurity, digital infrastructure, and enterprise-level deployment.
A few major players include CrowdStrike, Tenable, Palo Alto Networks, Microsoft, Qualys, Rapid7, CyCognito, Censys, IONIX, Bitsight, SecurityScorecard, Bugcrowd, HackerOne, IBM, Trend Micro, Outpost24, Google Cloud, Cisco, Hadrian, and UpGuard.
ASM refers to solutions and services that are used to find, track, and analyze digital assets to detect any known, unknown, and unmanaged security threats.
ASM finds exposed assets, whereas vulnerability management finds and remedies vulnerabilities on known assets.
Examples of some major applications are asset discovery, vulnerability management, threat intelligence, risk and compliance management, cloud monitoring, and third-party risk management.
A few of the key barriers to market entry are high deployment costs, complex IT infrastructure, integration issues, lack of cybersecurity experts, and many security findings.
The cloud deployment segment is expected to register a CAGR of 31.50% during the forecast period, due to rising cloud, SaaS, and distributed IT adoption.

Download Sample Report of Attack Surface Management Market
Please fill out the form to request a customized copy of the research report.


